
Lizenziertes Online Casino mit Slots, Sportwetten & Live Casino
August 5, 2026Founding of YouTube A Short History
September 2, 2026Network-based instruments like TLS inspection tackle knowledge in transit, whereas software inspection and SBOM/CBOM evaluation tackle embedded cryptography and information at relaxation. No single particular person should be succesful of generate, distribute, and use keys with out oversight. This principle, cut up control, is enforced via a couple of overlapping mechanisms. Separation of duties divides the lifecycle throughout distinct roles (crypto officer, key custodian, operator, auditor) so that nobody function spans technology, use, and audit. Twin https://chinanews777.com/uninterrupted-mobile-campaign-management-with-linken-sphere.html control and break up data require two or more licensed people to behave collectively for delicate operations, in order that no individual can activate or export a protected key alone.
Different Credentials: Issues, Steering, And Finest Practices
Early Greeks used transposition ciphers (a kind of encryption) to protect info from falling into enemy hands. In trendy times, and with the arrival of the information age, encryption has turn out to be an indispensable device to guard data and applications. Initially used primarily in banking and monetary functions, its adoption has turn into widespread throughout the digital transformation area, turning into a mandated requirement in lots of regulated industries. Mechanisms that permit approved entities to replace and retrieve the keys saved within the operational reminiscence.
This follows the principle of securing knowledge at relaxation and is useful for reconstructing a key from archived keying information. Cryptographic algorithms apply these algorithms together of keys, which serve as a secret information to complete the algorithmic operations appropriately. And these keys require administration as a part of ongoing cyber hygiene — which is what we’ll focus on in in this article. Finery Markets’ software is non-custodial and is offered solely to licensed institutional entities that act as unbiased operators of their own environments. All counterparties are solely liable for establishing and maintaining their very own bilateral buying and selling and settlement relationships.
Guaranteeing Data Integrity With Hash Capabilities

Within SAP Cloud Integration for data companies, sure information is encrypted to make sure privacy, hold it free from corruption, and maintain entry management. Keyfactor’s platform addresses the cryptographic key management challenges outlined on this information through an built-in suite of solutions. Combining each discovery approaches provides the comprehensive visibility that effective key administration requires.
Powering Trust In Skills — Competency-based Training Community (c-ben)

With Out the use of a secure storage device with correctly applied encryption and encryption keys, data may simply fall into the enemy’s arms. A root key is the topmost key in a Public Key Infrastructure (PKI) hierarchy, which is used to authenticate and sign digital certificates. It is actually an uneven key-pair with a length typically between 256 and four,096 bits depending on the digital signature algorithm used.
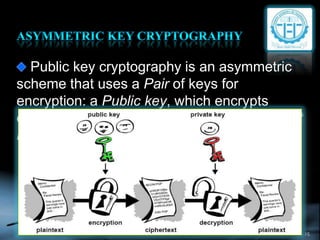
Solely the particular person who is supposed to get the message and has the proper private key can read the message. Whereas the basic public key may be freely shared with anybody, the recipient should maintain the personal key secret. Each are wanted to decrypt the info and communications, and the private key cannot be mathematically derived from the general public key, despite their linkage. For this purpose, asymmetric encryption is considered a extra strong and flexible strategy to encryption, despite being more computationally intensive. This mannequin underpins most blockchain methods, digital wallets, and secure web communications.
- Collectively these controls make certain that the failure of anybody person, whether or not malicious or merely careless, isn’t enough to compromise a key.
- In this blog collection, I will continue this dialogue by offering a more in-depth take a glance at the fundamentals of encryption keys and key administration mode classifications, together with related use instances.
- Encryption key administration is a vital side of ensuring information security.
- Authorities and industry regulatory entities around the globe have stepped up enforcement efforts to ensure the protection of knowledge and the privateness of the person whose information is being collected.
Access In Jail Initiative – Jstor
The security officer manages the keys based on the organization’s safety guidelines and procedures. The transition to post-quantum cryptography requires planning at present, even earlier than quantum computers are operationally viable. Organizations ought to start testing post-quantum algorithms, assessing their key inventories for quantum vulnerability, and constructing the crypto-agile architectures that can enable fast algorithm replacement when requirements finalize. Effective key administration rests on a stack of specialised hardware, entry controls, and operational records, most of which keep invisible until one thing breaks or an auditor asks to see them. To be taught more on the basics of encryption keys and key administration modes, you can download my white paper, “Unlocking the True Value of Encryption and Key Management Modes for Military Knowledge Storage Functions” or contact me at

